BehMon

Traffic analysis

Know who talks to whom, and how much

When a link fills up, the next question is “who?”. BehMon collects flows from your routers and firewalls, keeps the trend, and turns unusual behaviour into alerts.

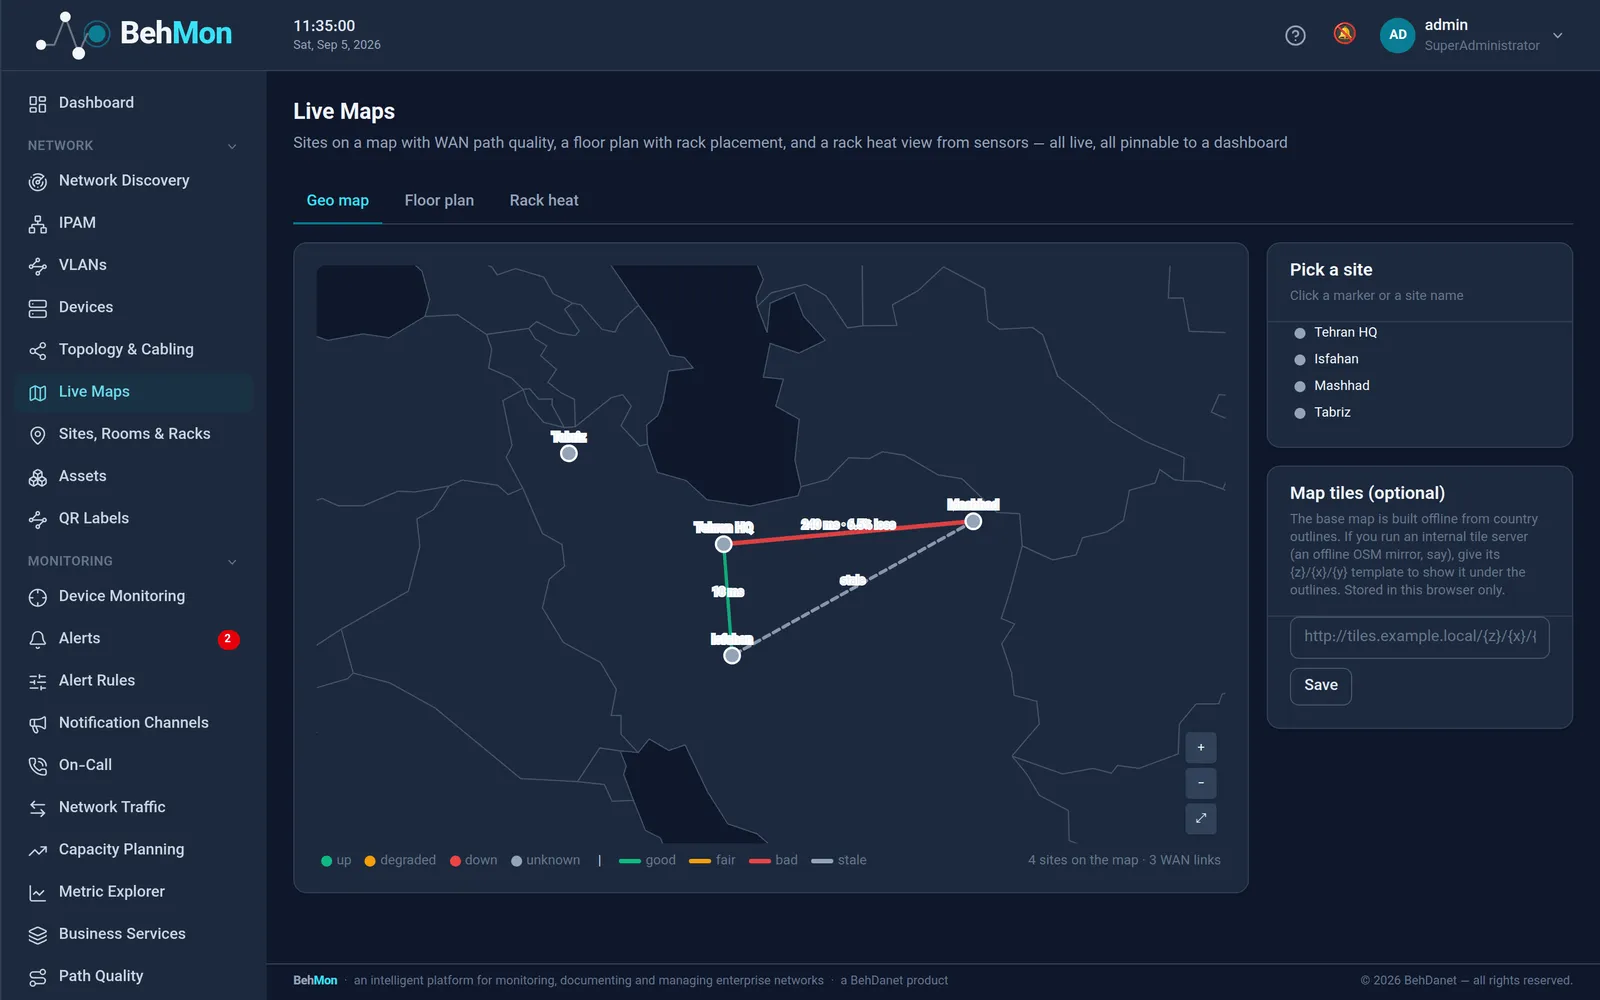
BehMon live site map with WAN link quality

NetFlow, IPFIX and top talkers

Flows arrive on one UDP port from any exporter, with v9/IPFIX templates and IPv6 endpoints.

  • Top sources, destinations and ports for any window
  • Hourly traffic history with a trend chart
  • Per-exporter growth feeding the capacity forecast

Behavioural detection (NDR-lite)

Four detectors run over the same flow data; each raises an ordinary alert that resolves itself when the behaviour stops.

  • Scan patterns
  • Volume deviation from each host's own baseline
  • Private-to-public flows shaped like exfiltration (critical)
  • First-seen destination ports on hosts with history

Syslog and SNMP traps

Device logs (RFC 5424 and BSD) and SNMP traps are stored and searchable in the same platform; linkDown/linkUp traps open and close interface alerts directly.

SIEM and ITSM integration

Every alert event can go to your SIEM as CEF over syslog, and alerts can be linked to your ticketing system.

Frequently asked questions

What do we need for traffic analysis?

Just point your router or firewall's NetFlow v5/v9 or IPFIX export at the BehMon server. No taps or port mirroring required.

See your own network in BehMon

Book an online demo, or install the 30-day trial on your own server. Our engineers will be right there with you.